Category: Thought Leadership

  • How Website Security Breaches Destroy Search Rankings

    How Website Security Breaches Destroy Search Rankings

    Search engines are trust-evaluation systems, and a website security incident is fundamentally a trust-destruction event that cascades through every layer of the discovery pipeline — crawling, indexing, rendering, and ranking — simultaneously. When you manage websites for clients, understanding this mechanism isn't optional; it's the difference between advising reactively after traffic collapses and advising proactively before discoverability is ever at risk. Google Safe Browsing blacklisted over 1.2 million sites in 2022. Flagged sites experience 60–95% organic traffic loss within 24–72 hours. And yet most agencies still treat security and SEO as separate line items on a proposal — separate teams, separate tools, separate conversations with clients. The causal chain is direct and measurable: compromise → indexing corruption → ranking loss → traffic collapse → revenue destruction. If you're not monitoring for security events as part of your technical SEO delivery, you're missing the root cause of failures that no amount of content optimization or link building can fix.

    How Do Security Incidents Directly Destroy SEO Performance for Your Clients?

    The damage operates across four distinct but simultaneous vectors, and understanding each one gives you the language to explain to clients why security monitoring belongs in every retainer — not as an upsell, but as a foundation.

    Clean indexing corruption through spam injection is the most common and least visible threat. Japanese keyword hacks, pharma hacks, and doorway pages get indexed as legitimate content under your client's domain, diluting topical authority and triggering manual actions in Google Search Console. In April 2022, over 500,000 WordPress sites were compromised via plugin vulnerabilities (Wordfence), with indexing disrupted for an average of 45 days. These injections are deliberately cloaked — visible only to crawlers, invisible to administrators — meaning they persist for months while your client's domain authority erodes. For a deeper look at how these attacks operate, this breakdown of SEO spam injection and pharma hacks maps the full attack lifecycle.

    Crawl interruption from resource hijacking compounds the problem. DDoS attacks and cryptominers cause repeated 5xx errors; Googlebot reduces crawl frequency and eventually drops pages entirely. Cloudflare's 2023 data found 18.5% of global websites faced DDoS attacks in Q2 2023. When your client's site becomes unreachable during a crawl window, the damage is silent — no error notification, just pages quietly disappearing from the index. Malicious bots consuming crawl budget is a related mechanism worth understanding in detail.

    Rendering compromise through malicious JavaScript destroys Core Web Vitals — INP, LCP, and CLS — in ways that directly intersect Google's Page Experience ranking signals. Injected cryptomining scripts don't just slow pages; they make them functionally unrankable. And reputation destruction via Safe Browsing blacklisting obliterates click-through rates overnight. The interstitial warning "This site may harm your computer" propagates across browsers, antivirus tools, and email filters simultaneously. British Airways didn't achieve full organic recovery until 2023 — five years after their 2018 incident.

    Tools like seeshare automate scanning across multiple client sites so you can detect these issues before they cascade into ranking loss, rather than discovering them weeks later in a traffic report you can't explain.

    What Is the Connection Between Website Security and Indexing Failures?

    This is the intersection most agencies miss entirely, and it's where your advisory authority gets built. Hacked sitemaps, compromised robots.txt and .htaccess files, and injected noindex tags are security events that manifest as indexing events. When a client asks "why did our indexed page count spike by 3,000 overnight?" the answer is almost never a CMS glitch — it's usually a compromise injecting cloaked content visible only to crawlers.

    The strategic concept your team needs to internalize is selective permeability: your client's infrastructure should be hardened against threats while remaining transparent to search engines. This is harder than it sounds because legitimate security tools frequently cause self-inflicted SEO damage when misconfigured.

    Security ToolSecurity BenefitSEO Risk When MisconfiguredMitigation Strategy
    **Cloudflare Pro/Business**DDoS protection, WAFJS challenges block Googlebot entirelyConfigure verified bot bypass rules
    **Sucuri**Malware scanning, blacklist monitoringMinimal — SEO-aware by designEnsure firewall doesn't cache stale pages
    **Wordfence**Endpoint firewall, malware scanRate limiting throttles crawl frequencyWhitelist known crawler IP ranges
    **Akamai Bot Manager**Sophisticated bot classificationBehavioral analysis misclassifies crawlersAllow-lists with reverse-DNS verification

    This table should be part of every client onboarding conversation. When you configure security tooling for a client, you're simultaneously making decisions about their discoverability. Understanding how search engines assess trust and safety signals helps you explain this dynamic with authority.

    Why Does the Security–SEO Gap Persist in Agency Operations?

    The gap persists because most agencies inherited siloed workflows. Your SEO team optimizes crawlability without understanding attack surfaces. Your security recommendations (if you make them) focus on infrastructure without accounting for bot behavior. Neither workflow monitors the overlap — the moment a security event becomes an indexation event.

    The data that should unify these disciplines is compelling: 82.3% HTTPS adoption as of August 2023 (W3Techs), with Google's Transparency Report confirming over 95% of HTTPS sites are prioritized in rankings. Meanwhile, 43% of cyberattacks target web applications (Verizon DBIR 2023), and organic search drives 30–50% of e-commerce revenue. A deindexing event isn't a technical inconvenience — it's an existential revenue threat for your client and a retention risk for your agency.

    The agencies pulling ahead in 2024 and into 2025 are the ones treating security and technical SEO as a single discipline — because operationally, they are.

    How Do You Recover a Client's Search Rankings After a Compromise?

    Recovery follows a predictable but painful sequence. First, contain and audit: identify the vector, then assess SEO damage via Google Search Console's Security Issues report, Manual Actions, and anomalous indexation spikes. Second, clean and reclaim: remove injected content and URLs, disavow toxic backlinks accumulated during the compromise window, and submit a reconsideration request. Google's review process is manual and backlogged. Third, monitor with realistic timelines — and set those expectations with the client before they check traffic daily.

    Recovery PhaseTypical DurationAgency Action
    **Detection to containment**Hours to daysRun immediate scan; isolate compromised components
    **Cleanup and reconsideration**1–4 weeksRemove spam URLs, submit reconsideration, disavow toxic links
    **Indexing normalization**30–90 daysMonitor Search Console for re-crawling; track indexed page count
    **Authority recovery**3–18 monthsRebuild trust signals; some domains never fully recover

    The asymmetry is stark: a compromise takes hours; recovery takes months, and some domains never fully regain authority. This asymmetry is your strongest argument for proactive monitoring. A baseline scan costs less than a client lunch per month and gives your clients visible proof of protection — while giving your agency documented evidence of the value you deliver.

    What Proactive Measures Protect Your Clients' Organic Performance?

    The framework for client conversations maps established security controls to specific discoverability outcomes. Enforce HTTPS with HSTS headers — baseline trust signal and confirmed ranking factor. Deploy file integrity monitoring on web-accessible directories so changes outside the deployment pipeline trigger immediate alerts. Implement Content Security Policy headers to block XSS rendering attacks and injected cryptominers simultaneously. Whitelist search engine crawler IPs in WAF configurations, validated via Googlebot reverse-DNS verification. Automate CMS and plugin updates with staged rollout — unpatched WordPress plugins remain the top spam injection vector in 2024.

    With seeshare, you can run a baseline scan before a client pitch to demonstrate the value you bring, then map findings to specific compliance controls like OWASP Top 10 and NIST CSF 2.0 so the conversation moves from abstract risk to concrete, actionable recommendations delivered under your agency's brand. A thorough website security assessment is the starting point for every client relationship where organic performance matters.

    Frequently Asked Questions

    Can website security issues cause Google to deindex a client's site? Yes. Google Safe Browsing flags trigger interstitial warnings and can lead to full deindexing. Spam injection from compromises can cause manual actions that remove pages from search results entirely. As of 2024, Google's automated systems detect most compromised sites within 24–48 hours.

    How long does it take to recover search rankings after a compromise? Typically weeks to months. WordPress spam injection disrupts indexing for an average of 45 days. Severe incidents involving Safe Browsing blacklisting can require 6–18 months for full recovery. Some domains never fully recover authority — which is why the proactive monitoring conversation matters more than the recovery conversation.

    How do I know if a client's site has been compromised in a way that affects SEO? Run site:clientdomain.com queries to detect pages nobody created. Check Google Search Console weekly for Security Issues and Manual Actions. Monitor for anomalous spikes in indexed page counts — this is the hallmark of spam injection and one of the earliest detectable signals.

    Should I temporarily block search engines from indexing a client's site during a compromise? In specific scenarios, temporarily noindexing actively compromised pages prevents Google from indexing spam content under the client's domain. But this should be surgical — applied only to affected URLs — and reversed immediately after cleanup. A site-wide noindex during remediation creates a second crisis.

    Do legitimate security tools ever harm SEO performance? Frequently, when misconfigured. Cloudflare's "Under Attack" mode serves JavaScript challenges Googlebot cannot execute, effectively deindexing sites during activation. Aggressive WAFs throttle crawl rates. The goal is selective permeability — hardened against threats, transparent to search engines.

    Security Is Technical SEO — And the Agencies Who Understand This Win

    The agencies building durable competitive advantages in 2024 and beyond are the ones that unify security monitoring and SEO monitoring into a single operational view — where an anomalous spike in indexed pages triggers both a security alert and an SEO conversation. This isn't a theoretical position. It's an operational structure that directly reduces client churn, strengthens proposals, and creates advisory authority that commodity SEO providers can't replicate.

    seeshare gives you the infrastructure to deliver this unified view across every client in your portfolio — automated scanning, compliance mapping, branded reporting, and the data you need to brief clients on where they stand before they ever have to ask. Run a baseline scan on your next prospect's site before the pitch. Show them the findings. Let the data make the case for why security belongs in every engagement — and why your agency is the one to deliver it.
  • How Search Engines Assess Website Trust and Safety

    How Search Engines Assess Website Trust and Safety

    Search engines assess website trust and safety through a multi-layered system that synthesizes technical security signals, spam detection, content quality evaluation, and temporal reputation data into real-time ranking decisions. Google Safe Browsing alone protects over 5 billion devices and flags approximately 40,000 unsafe sites weekly — and understanding how a single Safe Browsing flag affects organic traffic gives you the clarity to protect client visibility proactively. For agency owners, MSPs, and consultants managing client websites, understanding this complete pipeline positions you as the advisor who delivers clarity before problems surface. Most public explanations cover only one layer in isolation. This piece maps the complete four-layer trust model search engines actually use, where security and SEO permanently converge, and what's shifting in the next 12–24 months — so you can brief clients with precision no competitor is offering.

    Why Trust Is a Four-Layer Problem, Not a Single Checkbox

    The instinct for most agencies is to treat trust as a binary state: the client's site has HTTPS, so it's "secure." Or it hasn't been flagged, so it's "trusted." But search engines evaluate trust across four overlapping dimensions — technical security, spam and manipulation detection, quality and reputation perception, and contextual and temporal trust — each running through entirely separate detection systems with different signals, thresholds, and recovery timelines.

    What makes this genuinely complex is that trust is contextual and non-binary. Roughly 60–70% of sites flagged for malware distribution are otherwise legitimate sites affected through a single unpatched plugin — not purpose-built attack domains. A client's site can be technically secure yet editorially thin, or contain expert content while running a third-party script with known security findings. Each layer can independently suppress visibility.

    For agencies, this creates a strategic advantage. If you can assess all four layers in a single assessment rather than checking isolated boxes, you're offering something most competitors simply don't. Tools like seeshare automate scanning across multiple client sites and map findings to specific compliance controls, giving you the infrastructure to deliver this kind of comprehensive evaluation at scale — not just one-off spot checks.

    How Do Search Engines Evaluate Technical Security?

    Google Safe Browsing is integrated into approximately 85% of modern browsers — Chrome, Firefox, and Safari — making it the de facto infrastructure layer for web safety (StatCounter, 2023). Microsoft runs a parallel system through SmartScreen, covering the Edge and Windows ecosystem with URL and download reputation analysis. Industry estimates suggest even privacy-focused engines like DuckDuckGo rely on upstream Safe Browsing data, meaning a flag in one system likely cascades across virtually the entire browsing ecosystem.

    Core technical signals include HTTPS implementation and certificate validity (used by 95% of top-ranking sites and a confirmed ranking signal since 2014), IP reputation, hosting neighborhood analysis, DNS configuration, and the presence of malicious scripts or deceptive iframes.

    One risk that's particularly relevant for agencies managing small-business clients: cheap shared hosting where hundreds of sites share an IP range creates ambient distrust signals that are difficult to diagnose. If a neighboring site on the same IP gets flagged, your client's site inherits reputational drag — even though nothing changed on their end. This is the kind of finding that continuous security scanning surfaces and manual reviews miss.

    Signal CategoryGoogle Safe BrowsingMicrosoft SmartScreenPrivacy Engines (DuckDuckGo, Brave)
    Malware/Phishing DetectionReal-time hash-based + AIURL + download reputationRelies on upstream Safe Browsing data
    HTTPS EnforcementRanking signal since 2014Browser warning onlyAutomatic HTTPS upgrade (Brave, per industry estimates)
    IP/Hosting ReputationYes, neighborhood analysisLimitedMinimal
    Coverage~85% of browsersEdge/Windows ecosystemGrowing but fragmented
    Update FrequencyMoving to real-time (2024–25)PeriodicInherited from data sources

    How Do Spam and Manipulation Detection Systems Actually Work?

    Google's 2023 Webspam Report revealed spam content affected 60 billion pages, with 90% detected and removed before reaching users. But the adversarial dimension is what most agency conversations miss entirely. Attackers don't just create obviously spammy sites — they use cloaking to serve search engines clean content while delivering malware to users, time-delayed payloads that activate after indexing, and conditional redirect chains that target users based on geography or device. Understanding these techniques positions you to identify them early.

    This is the domain of SEO spam injection — where attackers use a legitimate client domain's authority to distribute thousands of unauthorized pages. Search engines are effectively seeing a different version of the web than your clients' users are, and the March 2024 core update dissolved the boundary between spam systems and core ranking, meaning spam-adjacent signals now directly influence organic visibility in ways they didn't before.

    For your client conversations, this means systematic scanning reveals trust signal issues that aren't visible from a surface-level review. With seeshare, you can run a baseline scan before a client pitch to demonstrate specifically where hidden manipulation or compromised scripts are eroding their search visibility — turning abstract risk into concrete, visible findings.

    What Is the Relationship Between Website Security and SEO?

    When a site is affected by a security incident, understanding the detection-to-impact timeline is what enables a fast, effective response. Industry estimates suggest Google detects affected sites within 24–48 hours and interstitial warnings can appear shortly after. Understanding this timeline — and having continuous monitoring in place — gives you the window to respond effectively and preserve organic visibility. Industry data suggests unresolved flags can reduce traffic by 60–95%, which is why early detection matters. The APWG reported a 47% year-over-year increase in phishing attacks through 2023 — staying ahead of these trends through continuous monitoring gives your clients a clear advantage.

    But the convergence between security and SEO runs deeper than incident response. Google's E-E-A-T framework evaluates editorial credibility through algorithmic classifiers like the Helpful Content System, author attribution, and transparent editorial policies. A site that experiences SEO data corruption from a security incident doesn't just lose traffic — it loses the compounding trust signals that took months or years to build. Understanding this dynamic is what makes proactive monitoring so valuable.

    Impact PhaseTimelineTraffic EffectRecovery Requirement
    Initial Detection24–48 hoursRanking suppression beginsIdentify and isolate the issue
    Safe Browsing FlagHours after detectionSignificant organic traffic loss (up to 60–95%)Full malware removal + reconsideration request
    Active Recovery2–4 weeks minimumGradual restorationClean scans + Search Console verification
    Temporal Trust Recovery3–6+ months (industry estimates)Lingering reputational dragConsistent clean signals over time

    For agencies, these numbers are the most powerful data points you can put in a proposal. Proactive scanning gives your clients visible, ongoing proof of protection — and the confidence that comes from knowing their digital presence is continuously monitored. That kind of clarity is what turns a service engagement into a long-term advisory relationship.

    What's Changing in Search Engine Trust Over the Next 24 Months?

    Three shifts are reshaping the trust landscape in ways that directly affect how you serve clients.

    Real-time Safe Browsing is already rolling out in Chrome, reducing the window between a site being flagged and users being warned from minutes to seconds. Real-time detection makes proactive scanning even more valuable — agencies with continuous monitoring in place can identify and address issues before visibility is affected.

    Verified entity identity is becoming critical. Google's Knowledge Panel claims, Merchant Center verification, and the trajectory toward W3C Verifiable Credentials all point toward a web where provable organizational identity influences trust scoring. Agencies who help clients establish and maintain these verified signals now will compound that advantage over the next several years.

    Regulatory acceleration is creating new service opportunities. The EU's Digital Services Act (fully enforced as of February 2024) and the UK's Online Safety Bill both set clear expectations for how organizations manage digital trust. Meeting these requirements positions your clients as trustworthy operators — and for agencies, compliance scanning that maps client findings to specific regulatory frameworks becomes a value-added service line, not an afterthought.

    Frequently Asked Questions

    How does Google Safe Browsing affect my client's search rankings?

    Early detection through continuous monitoring helps you address Safe Browsing flags before they affect organic visibility — industry data suggests unresolved flags can reduce traffic by 60–95%. The flag operates as a separate system from core ranking algorithms, but the practical effect on visibility is significant — users see interstitial warnings that prevent normal access through search. Recovery requires a clean scan, a reconsideration request through Google Search Console, and a minimum two-to-four-week waiting period.

    What are three signs a client's website might be flagged as unsafe in search results?

    Industry estimates suggest three common indicators: suspicious URL patterns with encoded redirects, missing or expired HTTPS certificates, and Google's "About this result" panel showing warnings or limited information about the site. Behind the scenes, triggers include the presence of known malicious scripts, hosting on IPs associated with flagged sites, and behavioral signals like conditional redirects that serve different content to crawlers versus users.

    Can a malware flag hurt SEO even after it's resolved?

    Yes. Search engines maintain temporal trust signals, which means industry estimates suggest a security incident can create lingering reputational effects for three to six months beyond the resolution date. The good news is that the recovery trajectory is within your control — how quickly the issue was addressed, whether subsequent scans remain clean, and the consistency of positive signals all influence how rapidly trust is restored.

    How do search engines determine if a website is safe or trustworthy?

    Through a four-layer synthesis: technical security signals (HTTPS, Safe Browsing status, IP reputation), spam and manipulation detection (SpamBrain, cloaking detection, link scheme analysis), quality and reputation perception (E-E-A-T signals, editorial credibility), and temporal trust data (domain history, publishing consistency, recovery patterns after incidents).

    Which search engine is safest — and does the distinction matter?

    The more relevant distinction is between browsers and search engines. Chrome and Firefox both use Google Safe Browsing; Edge uses Microsoft SmartScreen. Since Safe Browsing is integrated into 85% of modern browsers, a flag in Google's system effectively reduces visibility across nearly all browsing contexts — making the search-engine-specific distinction less meaningful than the browser-infrastructure reality.

    Building Trust as a Compounding Asset

    The agencies that will differentiate over the next two years are the ones treating search engine trust as a four-layer, continuously maintained asset — not a single checkbox. That means unifying security and SEO monitoring into a single reporting pipeline, assessing technical security alongside content quality and spam signals, and giving clients visible, ongoing proof that their digital presence is protected.

    seeshare gives you the infrastructure to do exactly that: automated scanning across your client portfolio, findings mapped to compliance frameworks, and white-label reports you deliver under your agency's brand. Rather than responding reactively to flags, you walk into every QBR with data that demonstrates the value you're delivering — and the trust you're compounding on their behalf.

    Start with a baseline scan on a client site this week. Use the findings in your next proposal or review meeting. The data gives you a clear, shareable picture of where that client stands — and positions you as the advisor who brought clarity to the conversation before anyone else in the room.

  • How Malicious Bots and Fake Pages Destroy Crawl Budget

    How Malicious Bots and Fake Pages Destroy Crawl Budget

    Crawl budget abuse occurs when unauthorized bots consume a website's finite search engine crawl allocation — the combination of crawl rate limit and crawl demand — by injecting fake pages, generating spam URLs, or manipulating parameters so that search engines spend resources on worthless content instead of discovering and refreshing the pages that drive revenue. For agencies managing client websites, understanding this as a single connected chain — from bot activity through page injection, crawl allocation shifts, and indexing effects — is what enables faster diagnosis and sharper client advice. Agencies that map this chain proactively position themselves with a level of authority that sets them apart.

    Industry surveys consistently suggest that a significant percentage of SEO professionals have encountered crawl budget issues tied to bot traffic or spam content, with many reporting measurable ranking impacts. Imperva's annual Bad Bot Report has documented that automated bot traffic accounts for a substantial share of all web requests — and the proportion classified as unauthorized continues to grow. The signals — declining impressions, slower indexing, unexpected ranking shifts — overlap with dozens of other SEO issues, which is exactly why agencies that understand this chain can diagnose root causes faster and advise clients with clarity that competitors can't match.

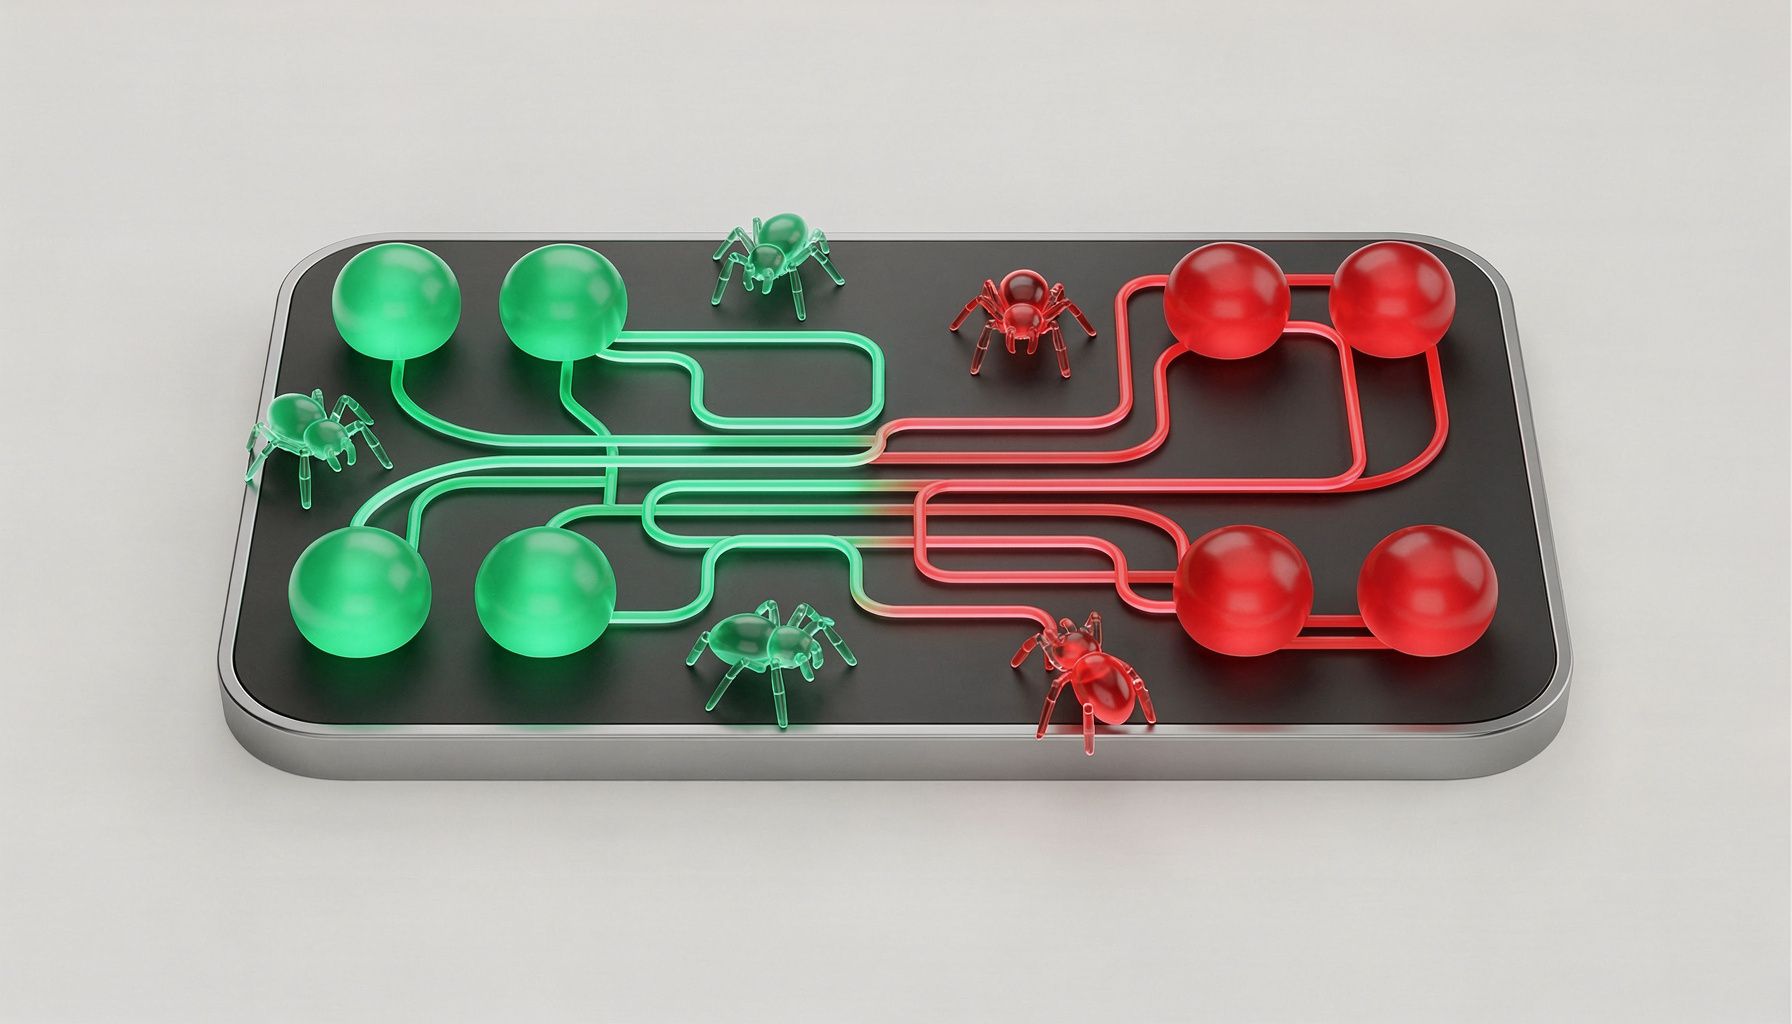
    A minimal 3D cutaway of a website server room where translucent Googlebot spiders crawl along illuminated pathways, some paths blocked by glowing red fake page nodes siphoning the spiders away from legitimate green content nodes

    How Do Malicious Bots Actually Drain Crawl Budget?

    Understanding the specific vectors helps you explain to clients exactly what's happening on their sites — and why standard SEO fixes won't resolve an underlying security issue. The six primary vectors operate at different scales, but they all converge on the same outcome: wasted crawl allocation.

    Injection MethodMechanismTypical Scale
    SEO spam botsTarget unpatched CMS weaknesses to generate doorway pages for pharma, gambling, or counterfeit keywords10,000–500,000+ injected URLs
    Parameter manipulationAppend query strings to existing URLs, creating infinite crawl traps (e.g., `?sort=price&page=1…∞`)Millions of duplicate URL variations
    Cloaked content injectionServe spam exclusively to crawlers while showing clean pages to humansHundreds to thousands of pages
    UGC abuseAutomated fake profiles, forum posts, or keyword-stuffed reviewsTens of thousands of pages
    Subdomain hijackingLeverage dangling DNS records to host fraudulent content under a trusted domainEntire subdomain indexes
    Japanese keyword hackAuto-generate directories with foreign-language titles, monetized through affiliate redirectsThousands of directories

    For a deeper look at how spam injection specifically degrades search authority, see our breakdown of how pharma hacks kill search rankings.

    A detection gap worth understanding: Google can index injected pages quickly, and on high-volume sites with millions of legitimate URLs, thousands of injected spam pages blend into normal index coverage reports. Tools like seeshare that automate scanning across multiple client sites give you an early-warning system that manual checks can't replicate — helping you catch anomalies before they compound into measurable changes.

    What Does Fake Page Generation Do to Organic Traffic?

    The downstream effects follow a predictable cascade. Index bloat dilutes the ranking signals that Google associates with your client's domain. Legitimate pages go stale because Googlebot exhausts its crawl allocation on spam. Domain authority erodes as Google's quality algorithms associate the domain with thin, duplicative, or deceptive content.

    Patterns observed across the industry illustrate the cascade. E-commerce sites with large product catalogs see unauthorized bots generate thousands of fake product pages that consume crawl budget before anyone notices the index coverage spike. News and media publishers face scraped articles republished on duplicate subdomains, fragmenting ranking signals. Smaller content sites experience ranking drops after automated tools generate hundreds of low-value posts that trigger Google's quality algorithms. These are recurring patterns agencies encounter across verticals.

    As of 2024, generative AI has significantly reduced the cost of creating plausible injected content. The result is that injected pages increasingly resemble legitimate content rather than obvious keyword-stuffed spam, making detection harder without dedicated monitoring. This distinction matters when clients ask about AI-generated content and SEO: the issue isn't authorized AI content created with editorial oversight — it's unauthorized fake page generation at scale that produces thin and duplicate content problems far beyond normal duplication. For agencies, understanding this intersection of security compromises and corrupted SEO data helps you diagnose root causes accurately.

    An isometric flowchart showing five connected floating platforms in a descending cascade — the first platform glows red with bot icons, flowing down through fake page generation, then crawl budget depletion shown as a shrinking pool, then index bloat as an overflowing container, and finally ranking loss depicted as a downward-trending graph — with color-coded data streams connecting each stage

    Why Do Security Teams and SEO Teams Keep Missing This?

    Here's the organizational pattern worth recognizing: SEO teams don't own server security, and security teams don't understand crawl economics. Fewer than 5% of organizations operate with integrated Security-SEO operations. This means the attack chain falls into a gap between two teams that rarely share dashboards, metrics, or incident response procedures.

    CMS monoculture compounds the pattern. WordPress powers roughly 43% of the web, which means a single plugin finding creates a broad exposure area across millions of sites simultaneously. Understanding how these web application security findings cascade into SEO damage is what separates agencies that advise proactively from those that react after the impact is visible.

    Most organizations also never analyze server-level crawl logs. GSC data is sampled, delayed by two to three days, and incomplete. Without authoritative server log analysis, teams lack visibility into what bots are actually requesting. On the regulatory side, meeting EU Digital Services Act and EU AI Act compliance requirements — which now include bot-driven spam mitigation and transparency on AI-authored content — strengthens client trust and platform integrity.

    How Do You Detect and Recover from Crawl Budget Abuse?

    Recovery success correlates directly with detection speed. Proactive organizations that detect abuse early consistently achieve stronger recovery outcomes, and agencies that build proactive detection into their workflows are better positioned to deliver those results.

    PhaseActionWhy It Matters
    **Baseline**Crawl the entire site with Screaming Frog or Sitebulb; document total URL count, directory structure, parameter patternsCreates the source of truth against which anomalies are measured
    **Monitor**Pipe server logs into Splunk, ELK, or BigQuery; verify Googlebot via reverse DNS; track GSC index coverage ratios weeklyServer logs are authoritative and real-time — GSC alone is insufficient
    **Detect**Set automated alerts for crawl volume spikes, requests to unrecognized URL patterns, or sudden "Discovered – currently not indexed" increasesNear-real-time detection gives you the earliest possible window to respond
    **Remediate**Return `410 Gone` for injected URLs; patch the underlying finding *before* cleaning spam; harden CMS by deleting unused plugins, deploying WAF with bot rulesets, disabling XML-RPC, enforcing CSP headersBlocking via robots.txt doesn't de-index already-indexed pages; a `410` explicitly signals permanent removal
    **Recover**Track crawl stats, indexed page count, organic sessions, keyword rankings over 4–12 weeksIndustry estimates suggest recovery timelines vary, but addressing the underlying finding prevents reinfection

    Three common mistakes reduce recovery effectiveness. First, blocking injected URLs via robots.txt instead of returning 410 — blocking prevents crawling but doesn't remove already-indexed pages. Second, bulk disavowing links when the problem is content injection — different root causes require different solutions. Third, cleaning spam pages without patching the underlying finding, which leaves the same entry point available for repeat injection. For a more comprehensive look at the full recovery process, our guide on SEO recovery after a website hack walks through timelines and benchmarks.

    Should Agencies Advise Clients to Block AI Bots — and What Comes Next?

    AI crawlers like GPTBot, ClaudeBot, and Bytespider are becoming a parallel crawl budget consideration. They compete with Googlebot for server resources, and for smaller client sites with limited capacity, the impact can be material. The decision framework worth walking clients through weighs whether AI training data exposure benefits their brand against the real cost of server resource competition.

    Looking ahead to 2025–2027, dedicated "SEO Security" roles and tooling are emerging. The bot mitigation market is projected to reach $3.5 billion by 2027. For agencies, index integrity is becoming a first-class infrastructure concern — crawl health metrics belong in security dashboards, and organic search impact should factor into how findings are prioritized. Understanding why security and technical SEO are converging into one discipline positions your agency to lead that conversation.

    FAQ

    How do unauthorized bots affect my clients' SEO and search rankings? Unauthorized bots inject fake pages into a site's index, causing search engines to spend crawl budget on spam instead of legitimate content. This dilutes ranking signals and erodes domain authority — understanding the mechanism helps agencies diagnose root causes faster.

    What is crawl budget abuse and how do fake pages hurt organic traffic? Crawl budget abuse occurs when unauthorized bots consume a site's finite crawl allocation through spam URLs, parameter manipulation, or cloaked content injection. The resulting index bloat suppresses rankings for legitimate pages that drive revenue.

    How do I detect and recover from a Japanese keyword hack or crawl budget depletion? Start with server log analysis to identify unrecognized crawl patterns, then check index coverage for unexplained spikes. Remediate by returning 410 Gone for injected URLs, patching the finding that enabled injection, and hardening the CMS with WAF deployment and plugin cleanup.

    What are the biggest website security findings affecting SEO in 2024? AI-powered content injection at scale, parameter manipulation creating infinite crawl traps, subdomain hijacking via dangling DNS, and AI crawler competition for server resources are the most significant converging factors as of 2024.

    How do I protect client websites from SEO spam bots and injected content? Deploy a Web Application Firewall with bot-specific rulesets, implement continuous server log monitoring with anomaly detection, and establish URL baselines to catch injection early. Building cross-functional workflows where security findings inform SEO response closes the organizational gap most teams overlook.

    Treating This as One Connected Problem Is the Agency Advantage

    The most productive starting point is auditing server logs across your client portfolio for unrecognized crawl patterns and checking GSC index coverage for unexplained spikes. From there, ask your clients whether their security team and SEO team have ever shared a dashboard. If the answer is no — and it almost always is — you've identified the organizational gap your agency is positioned to fill. That conversation alone changes how clients perceive your value.

    seeshare gives you the infrastructure to deliver on that promise — baseline scans across client sites, branded reports that document security posture alongside crawl health indicators, and the continuous monitoring that turns reactive firefighting into proactive advisory. Starting with a baseline scan on a single client site gives you concrete findings to frame your next conversation and a foundation for the kind of ongoing value that strengthens client relationships.

  • How Website Hacks Destroy Search Rankings and How to Recover

    How Website Hacks Destroy Search Rankings and How to Recover

    When a website is compromised, search visibility follows a predictable multi-phase decline — Google detects compromised sites within 24–48 hours and begins suppressing rankings, yet full recovery takes 2 to 18+ months depending on site authority, compromise type, and response speed. For agencies and MSPs managing client websites, the most impactful gap you can close is the window between when Google knows a client site is compromised and when you know. According to aggregated Sucuri reports, the median detection time for site owners ranges from 70 to 200 days. Closing this gap puts you in control of the recovery timeline from day one.

    This piece maps the complete lifecycle — technical remediation, SEO recovery, and trust rebuilding — so you can advise clients with authority if a compromise occurs in your portfolio.

    What Does Google Actually Do When It Detects a Compromised Site?

    Google Safe Browsing flags over 40,000 websites weekly as unsafe, according to the Google Transparency Report from 2023. Browser interstitial warnings — those full-screen "This site may harm your computer" pages — cause a 12–25% traffic drop entirely independent of any ranking change. That's before algorithmic suppression even begins.

    There's a critical distinction your clients won't understand unless you explain it: manual actions and algorithmic suppression are two different mechanisms requiring two different recovery playbooks. A manual action appears in Search Console and requires a formal reconsideration request. Algorithmic suppression happens automatically through systems like SpamBrain and has no formal appeal process — recovery depends entirely on sustained signals of trustworthiness over time. Google Search Advocate John Mueller confirmed in September 2023 that "rankings drop immediately upon detection, even before owners are aware."

    Here's what this means for your agency: if you're running continuous monitoring through a tool like seeshare, you can detect anomalies and self-report through Search Console before Google's automated systems escalate their response. Self-detecting gives you a meaningful head start in the recovery timeline — you enter the process on your own terms, with documentation already in hand and remediation underway.

    What Does the Search Ranking Impact Look Like Phase by Phase?

    The impact follows a predictable sequence, though the timeline compresses or extends based on site authority and compromise type. Understanding each phase helps you set realistic recovery expectations with clients — and prevents the all-too-common scenario where a client assumes cleanup equals recovery.

    Phase 1 — Silent Compromise begins on day one and lasts until detection. Cloaked spam, hidden redirects, or doorway pages are injected — visible to Googlebot but invisible to site owners. As we've covered in our analysis of SEO spam injection and pharma hacks, the site may actually appear to gain traffic from spam queries — masking the erosion of legitimate rankings. The most common vectors map to OWASP Top 10 categories: injection attacks and security misconfigurations, particularly in CMS environments with outdated plugins. Knowing these common patterns helps you identify compromises faster. Knowing these common patterns helps you identify compromises faster.

    Phase 2 — Detection and Flagging is when Google's systems formally classify the site as compromised. Organic traffic drops 40–70% within the first two weeks of flagging, driven by quality score suppression, CTR collapse from "This site may be hacked" SERP warnings, crawl budget reallocation, and loss of rich results and sitelinks.

    Phase 3 — Deindexation occurs if the compromise remains unresolved. Google removes indexed pages — either surgically for compromised URLs or broadly across entire subdirectories. Backlink equity associated with deindexed pages diminishes significantly. Even after cleanup, pages that were deindexed rarely return to prior positions without sustained effort — which is why the speed and thoroughness of your response directly shapes the outcome.

    PhaseTimelineTraffic ImpactWhat Agencies Should Communicate
    Silent CompromiseDay 1 to detection (often 70–200 days)Masked by spam traffic gains"Here's how we separate real traffic trends from spam noise"
    Detection & Flagging24–48 hours post-Google detection40–70% organic loss within 2 weeks"Here's the timeline and what we can do right now to accelerate recovery"
    DeindexationDays to weeks if unresolvedBacklink equity loss, page removal"Each day of proactive cleanup shortens the recovery timeline significantly"
    Recovery & Trust Rebuilding2–18+ monthsSlow, non-linear restoration"Cleanup is the starting line — here's the full roadmap"

    How Long Does Recovery Actually Take — and What Determines the Timeline?

    This is the question your clients will ask first, and the answer requires nuance. Aggregated case study data from SEMrush, Ahrefs, and industry reports as of 2024 reveals a clear pattern tied to domain authority.

    Site Authority LevelRecovery to 80% TrafficRecovery to 95%+ Traffic
    High authority (DR 60+)2–4 months4–8 months
    Mid authority (DR 30–59)3–6 months6–12 months
    Low authority (DR < 30)6–12 months12–18 months, or requires sustained long-term effort

    These benchmarks assume prompt detection and thorough remediation. Kaspersky Labs' 2023 report found small websites take three times longer to recover than enterprises due to limited rapid-response resources — which is precisely the gap agencies fill. The variables that matter most are time-to-detection, compromise type (Japanese keyword spam, malware injection, and redirect hijacking each produce different damage patterns and SEO data corruption), completeness of cleanup, and speed of reconsideration request. The key takeaway for client conversations: reconsideration request approval does not equal ranking recovery. Manual action removal is the starting line — algorithmic trust rebuilding is a separate, months-long process that your agency can actively guide.

    What Is the Right Recovery Sequence — and Where Do Agencies Add the Most Value?

    The recovery protocol follows a strict order, and agencies that can execute it confidently differentiate themselves from competitors who treat security as someone else's problem. For a deeper dive into the full recovery framework, we've published a companion guide — but understanding how each phase depends on the one before it is essential.

    Recovery begins with containment and documentation. The evidence you preserve — compromised URLs, injected content, affected sitemaps — becomes the foundation for every step that follows. Google's webspam team evaluates reconsideration requests based on thoroughness, so forensic documentation is your client's credibility asset. File integrity monitoring tools like OSSEC or Tripwire help verify a clean state.

    With the site stabilized, the focus shifts to surgical URL management. Spam doorway pages need to be removed, but legitimate pages that were infected should be cleaned and resubmitted rather than bulk-deleted. Submitting fresh XML sitemaps with updated lastmod timestamps signals active maintenance to Google, preserves indexing equity, and feeds directly into backlink triage. Referring domains that severed links need outreach, and injected toxic backlinks need strategic disavowal.

    Two common missteps extend timelines unnecessarily: submitting a reconsideration request before remediation is truly complete (which reduces your credibility with Google's webspam team), and migrating to a new domain — where 301 redirects carry penalty signals while abandoning accumulated authority. In nearly all cases, recovering the existing domain is the strategically stronger path.

    Why Is Proactive Monitoring the Strongest Recommendation You Can Make?

    As of 2025, the landscape is compressing from both sides. Google's SpamBrain and AI-driven detection systems are identifying compromises faster, shortening the window before penalties take effect. At the same time, injected spam is becoming more sophisticated and harder to detect through pattern-based methods alone. The NIS2 Directive, enforced since October 2024, creates an opportunity to align website security with evolving compliance frameworks that build customer trust and strengthen your advisory relationship.

    For agencies, this means the detection gap — your primary controllable variable — demands proactive tooling. Running scheduled scans through seeshare across your client portfolio creates an early-warning system. Instead of discovering an issue when a client calls about traffic loss, you detect anomalies before Google escalates its response — shifting your agency from reactive firefighter to proactive advisor.

    Frequently Asked Questions

    Will Google penalize a client's site permanently after a hack? No — but recovery timelines are real and authority-dependent. High-authority sites typically reach 95%+ traffic within 4–8 months. Low-authority sites may take 12–18 months or never fully recover. Setting realistic expectations early protects your client relationship.

    Should a client change their domain after a hack? In nearly all cases, no. Recovering the existing domain is strategically superior. Migrating destroys accumulated authority, and 301 redirects transfer penalty signals to the new domain. The only exception is when the domain itself has been fundamentally compromised in reputation beyond recovery.

    How does a compromise affect Google Ads and Merchant Center accounts? A Safe Browsing flag can suspend Ads accounts and Merchant Center listings simultaneously. Re-verification is a separate process from Search Console recovery — another area where agency expertise accelerates the path back to normal operations.

    What is the single most important factor in shortening recovery time? Detection speed. Every day between compromise and detection extends the recovery timeline. Continuous monitoring — file integrity checks, crawl anomaly detection, Search Console security alerts — is the highest-ROI investment in recovery speed.

    Can Domain Authority recover after a compromise? Yes, but it lags behind ranking recovery. Restoring severed referring domain links through outreach and earning new authoritative backlinks are ongoing efforts that compound over time.

    Turning This Knowledge Into Client Value

    A website compromise requires security and SEO to be addressed in parallel from hour one. Your ability to articulate this lifecycle, set realistic recovery timelines, and execute the right remediation sequence is what positions your agency as the advisor clients trust most.

    The detection gap is narrowing from both sides, making continuous monitoring the strongest proactive posture you can recommend to clients. seeshare gives you the infrastructure to close that gap across your entire client portfolio: scheduled scans that flag anomalies before Google escalates its response, white-label reports that demonstrate proactive protection under your brand, and the visibility to advise clients with authority. Starting with a baseline scan on a client site gives you the clarity that every conversation in this article builds on.

  • How Hacked Websites Corrupt SEO Data and Cost You Money

    How Hacked Websites Corrupt SEO Data and Cost You Money

    SEO data corruption from website compromises is the systematic distortion of organic traffic metrics, backlink profiles, and crawl data caused by hidden malware infections — leading agencies and consultants to make marketing decisions based on fundamentally false information. For agencies, MSPs, and consultants managing client websites, this is a commonly overlooked factor in marketing data quality. The compromises that do the most damage aren't ransomware headlines — they're the quiet infections that distort every downstream marketing decision you make on a client's behalf. Over 60% of compromised sites are exploited specifically for SEO spam (Sucuri 2023), and 29% of businesses misallocate budgets due to corrupted SEO data (BrightEdge 2023). Website security isn't an IT problem. It's a marketing data integrity problem and a revenue problem. Agencies that recognize this are better equipped to advise clients with confidence.

    How Do Invisible Hacks Corrupt Your Clients' SEO Data?

    The reason these compromises evade detection — and the reason they're so dangerous to the agencies managing affected sites — is that different attack types destroy different SEO signals. No single check catches them all. If you're advising clients on SEO performance without understanding this taxonomy, you're working with incomplete information.

    Attack TypeSEO Data Corruption MechanismWhy It Evades Detection
    **Japanese Keyword Hack**Injects thousands of cloaked pages into Google's index, consuming crawl budget and inflating indexed page countsPages visible to Googlebot but hidden from site owners via cloaking
    **Pharma/Casino Spam Injection**Corrupts backlink profiles and topical relevance through hidden links and doorway pagesCode obfuscated in base64 within database entries or compromised plugins
    **Malicious Conditional Redirects**Google sees redirects to scam pages; admins see a clean siteConditional logic targets only search-referred or mobile visitors
    **Ghost/Referral Spam in Analytics**Fabricated sessions injected directly into GA measurement IDsGA's Measurement Protocol accepts data without server-side validation
    **Sitemap Poisoning**Modified `sitemap.xml` points Googlebot to thousands of hidden spam URLsSitemaps are rarely monitored post-deployment

    For a deeper technical breakdown of injection-based attacks, see our guide on SEO spam injection and how pharma hacks kill search rankings.

    The core detection problem is structural. Cloaking defeats visual inspection entirely — you can browse every page on a client's site and see nothing wrong while Googlebot indexes thousands of spam URLs. Security teams don't monitor Search Console. SEO teams don't audit server logs. And according to Sucuri's 2023 data, 70% of compromised sites go undetected for over a month, silently corrupting every metric your team relies on for client reporting and strategy.

    This is exactly where tools like seeshare change the equation for agencies. Rather than hoping your SEO tools and security tools happen to surface the same problem, seeshare provides continuous monitoring across client portfolios — catching the file modifications, misconfigurations, and findings that precede these SEO-corrupting compromises before they compound into months of bad data.

    How Much Does SEO Data Corruption Actually Cost Your Clients?

    Direct cleanup costs — $500 to $15,000+ depending on severity — are the easy number to quantify. The real damage is the cascade of bad decisions made from bad data before anyone realizes the data was poisoned.

    Consider what happens in practice. A client's compromised site shows a 150% traffic spike from injected spam pages and ghost sessions. Your team, understandably, reports strong organic growth. The client increases PPC spend to capitalize on momentum. A UK retailer called Purely Pets experienced exactly this scenario in 2023 — a WordPress compromise injected 300+ spam URLs, generated phantom traffic, and triggered a $10,000 wasted PPC campaign before anyone identified the root cause. The British Airways Magecart attack led to a reported $3 million in misallocated ad spend, per RiskIQ 2022.

    Then there's the reputational impact. Google Safe Browsing warnings reduce click-through rates by 60–95%. And here's what agencies need to understand about competitive dynamics: the rankings your client loses during a compromise get absorbed by competitors — and those competitors rarely give that ground back. Recovery takes 3–12 months even after complete remediation.

    For agencies, this isn't abstract. It's a direct threat to client retention. When a client's organic revenue drops and their analytics tell a false story, your agency's ability to advise effectively is directly affected. SEMrush's 2023 survey found that 18% of digital marketers report annual losses exceeding $50,000 from decisions driven by poisoned analytics — a stat worth citing in every client conversation about why website security and technical SEO are one discipline.

    How Do You Detect a Hack That's Designed to Stay Hidden?

    Detection requires deliberately looking through the attacker's lens — spoofing the bot perspective, cross-referencing data sources, and monitoring signals that most agencies check only reactively.

    The most reliable early-warning signal is Google Search Console's Coverage Report. Monitoring indexed page counts weekly for every client surfaces unexplained spikes of hundreds or thousands of pages — a primary indicator of Japanese keyword hacks or sitemap poisoning. This is where most agencies first notice something is wrong, but the Coverage Report alone won't tell you what Googlebot is actually seeing.

    That's where Googlebot-spoofed crawling comes in. Running Screaming Frog or Sitebulb configured with Googlebot's user-agent string reveals what cloaked attacks are actually serving to search engines. Comparing discovered URLs against your known site inventory surfaces pages you don't recognize — whether they indicate a compromise or an internal governance gap, both are worth finding. The crawl data also feeds naturally into analytics cross-referencing, which separates real traffic from ghost spam. Filtering GA4 for referral sources showing high session counts with 100% bounce rates, then validating against server logs, highlights discrepancies. Industry estimates suggest if GA4 shows sessions that don't appear in server logs, those sessions were injected through the Measurement Protocol — not from real visitors.

    Finally, backlink audits round out the detection picture by catching spam network involvement. A sudden influx of links from unrelated foreign-language domains in Ahrefs or SEMrush is a reliable indicator that a client's domain authority is being exploited for parasite SEO. Taken together, these four approaches — index monitoring, bot-perspective crawling, analytics validation, and backlink analysis — give you overlapping coverage that no single check provides on its own.

    For a comprehensive detection-to-recovery framework, our SEO after a website hack guide walks through the full timeline.

    Why Do Most Recovery Efforts Leave Lasting SEO Damage?

    Even when compromises are identified and malware removed, most recovery efforts fail to address the SEO damage — leaving ranking harm embedded in Google's index for months.

    The root cause is a disconnect between security remediation and SEO remediation. Teams remove malicious code but never request removal of spam URLs from Google's index, never disavow the toxic backlinks the attack generated, and never submit a reconsideration request. The malware is gone, but Google is still indexing thousands of spam pages and counting hundreds of toxic backlinks against the domain. This gap is compounded when teams accept the inflated traffic numbers at face value without questioning data integrity — reporting "recovery" based on metrics that were artificially elevated by the compromise itself, which leads to overstated KPIs and continued misallocation for months after cleanup.

    Ironically, overcorrection can introduce its own damage. Overly aggressive WAF rules that accidentally block Googlebot cause deindexation as a side effect of remediation, while broad disavow files that reject legitimate backlinks reduce domain authority unnecessarily. The result is that recovery efforts themselves become a source of ranking harm when security and SEO teams aren't coordinating closely.

    Industry estimates suggest the following general recovery timeline, though actual timelines vary by severity and response speed:

    Recovery PhaseTimelineKey Actions
    ContainmentDays 1–7Isolate compromise, remove malware, patch vulnerability, reset credentials
    Cleanup & ReconsiderationWeeks 2–6Remove spam URLs from index, disavow toxic links, submit reconsideration request, verify Googlebot access
    Ranking RecoveryMonths 2–6Monitor Search Console impressions, rebuild internal linking, publish fresh content to re-establish topical authority
    Full RestorationMonths 6–12+Domain trust signals normalize, organic traffic returns to pre-compromise baseline

    Understanding how security incidents destroy SEO rankings at a technical level helps you set realistic client expectations — and positions your agency as the team that prevented the problem rather than the one scrambling to explain it.

    Why Is Proactive Security Now an SEO Strategy?

    The threat landscape is escalating in ways that make reactive approaches untenable. Attackers now use LLMs to generate thousands of topically plausible spam pages — not obvious gibberish — making content-inspection detection far harder (Gartner 2023). Google's March 2024 Site Reputation Abuse policy signals increasing algorithmic intolerance for compromised sites. And the EU's Digital Services Act makes proactive security a compliance requirement — meeting it builds client trust and demonstrates operational maturity.

    For agencies, this convergence creates a durable competitive advantage. Building security monitoring into your SEO service model gives you a measurable ROI story that pure-play SEO agencies can't match. When you can show a client that continuous scanning costs less than a client lunch per month and gives them visible proof of protection — including branded reports under your agency's name — you've differentiated in a way that's hard to replicate.

    seeshare is built for exactly this workflow. With Sales accounts designed for agencies managing multiple client domains, white-label reporting, and scheduled scans that automate continuous monitoring, you can deliver security as an ongoing service — not a one-time project — and catch the compromises that corrupt SEO data before they compound into months of bad decisions.

    Frequently Asked Questions

    How long does it take to recover SEO rankings after a website hack?

    Full recovery typically takes 3–12 months depending on severity, speed of detection, and completeness of both malware removal and SEO remediation. The containment phase takes roughly a week, but ranking restoration — particularly rebuilding domain trust signals — can extend well past six months. Setting this expectation early protects your agency relationship.

    Can a website hack corrupt analytics data and lead to bad marketing decisions?

    Yes. Ghost spam, fabricated sessions, and inflated traffic from injected redirects routinely cause budget misallocation. BrightEdge's 2023 research found that 29% of businesses have made budget errors from corrupted data. For agencies, this means every traffic report you deliver from a compromised site reinforces false assumptions.

    Does Google permanently penalize hacked websites?

    Google distinguishes between manual actions (reversible via reconsideration request) and algorithmic trust erosion (harder to reverse). John Mueller noted in 2023 that spam links from hacked sites can "permanently damage a site's reputation with Google" even after cleanup — making prevention dramatically more cost-effective than recovery.

    What is the relationship between website security and SEO performance?

    Website security directly protects crawl budget, index integrity, backlink profiles, analytics accuracy, and Core Web Vitals — all core ranking inputs. As of 2025, treating these as separate disciplines leaves gaps that attackers specifically exploit. Our guide on why security and SEO are one discipline explores this convergence in depth.

    Three Things to Do This Week — and Why They Build Client Trust

    Start by auditing every managed client's Google Search Console Coverage Report for unexplained indexed page spikes — this surfaces the most obvious indicators of injection-based attacks. From there, run a Googlebot-spoofed crawl on each site and compare discovered URLs against your known inventory, which reveals what search engines are actually seeing versus what you see in a browser. Cross-referencing your clients' analytics traffic sources against server logs rounds out the picture by identifying injected ghost sessions that exist only in analytics, not on the server.

    Industry estimates suggest these three steps take less than an hour per client and give you something invaluable: the ability to walk into a client meeting and say "We verified your marketing data is clean" — or catch a compromise before the impact compounds.

    seeshare makes this operational across your entire client portfolio. Run a baseline scan before your next client pitch to demonstrate the value you bring. Use scheduled scans to automate continuous monitoring. Deliver white-label security reports that position your agency as the team that protects the data every other marketing decision depends on. That's how you turn website security from an afterthought into a retention engine.

  • Website Security and Technical SEO: Why They’re One Discipline

    Website Security and Technical SEO: Why They’re One Discipline

    Security-SEO convergence is the practice of managing website security controls and search engine optimization as a single integrated discipline, recognizing that the same infrastructure configurations that protect a site from threats also determine how search engines crawl, index, and rank it. If you manage client websites, understanding this convergence is essential — because search engine crawlers and malicious bots use identical HTTP mechanisms: they follow links, test URLs, and parse server responses. Defending against one frequently harms the other, and very few agencies monitor both sides for their clients. According to the Google Transparency Report (October 2023), over 1.5 million websites are flagged weekly for security issues — and a Search Engine Journal survey (April 2023) found that 62% of digital marketers have experienced traffic drops from security-related incidents. These numbers highlight the scale of the opportunity for agencies that can bridge both disciplines. The governance gap is structural. SEO lives under marketing. Security lives under IT. No shared KPIs, no common dashboards, no unified assessment framework. Agencies advising clients on either discipline in isolation have an opportunity to deliver more integrated, higher-value service.

    How Do Search Engine Crawlers and Attackers See Your Client's Site the Same Way?

    Both Googlebot and a malicious scanner arrive at your client's site through the same front door. They request URLs over HTTP, follow internal links, evaluate server responses, and map the accessible surface. The overlap is nearly total — and it creates an important dynamic to manage when your client's security team deploys protections without considering crawl impact.

    Aggressive bot mitigation measures like rate limiting, CAPTCHAs, and JavaScript challenges frequently block Googlebot without anyone noticing. A WAF-blocked Googlebot may lead to crawl disruptions that affect indexation and organic traffic within days. The fix — verified bot allowlisting via reverse DNS confirmation rather than user-agent strings alone — is non-negotiable, yet routinely overlooked because the people configuring the WAF don't track search console data.

    Real-world cases make this tangible for client conversations. In 2021, Target experienced DDoS-triggered 503 errors that wasted crawl budget and caused a 10% organic traffic dip. The British Airways Magecart attack triggered Safe Browsing warnings and produced a 15% ranking drop for key commercial terms that persisted for six months. These real-world examples illustrate how monitoring both surfaces positions your agency to identify compound issues early and deliver more complete client value.

    Tools like seeshare let you run baseline scans across client sites to surface exactly these intersections — security findings that have direct SEO consequences — before they escalate into ranking losses or Safe Browsing flags.

    Why Do Hacked Client Websites Lose Rankings — and How Long Does Recovery Take?

    According to Sucuri's 2022 Hacked Website Report, 60% of hacked websites had outdated CMS software. Compromised sites suffer malicious redirects, cloaked spam injection, and hidden pages that trigger Google manual actions. The WordPress ecosystem alone saw over 50,000 sites compromised in 2022 via outdated plugin security findings, resulting in 30–40% traffic losses that persisted months after cleanup due to trust signal degradation. Many of these compromises stemmed from outdated plugins — a category of findings that's straightforward to monitor proactively.

    As John Mueller (Google Search Advocate) stated in a September 2023 Q&A: "Security issues like malware or phishing can lead to manual actions or de-indexing."

    Here's the gap that most agencies miss: recovery isn't just "clean the malware." Rebuilding crawl trust, reclaiming lost link equity from poisoned redirects, and reversing Safe Browsing flags requires coordinated security and SEO remediation. When an agency handles a client's SEO but not their security posture — or vice versa — there's an opportunity to close the gap by addressing both dimensions together.

    Incident TypeSEO ImpactTypical Recovery Timeline
    Malware injection with Safe Browsing flagManual action, deindexation of affected pages3–6 months after cleanup
    Hidden redirect / cloaking via plugin-level finding30–40% organic traffic loss, link equity drain4–8 months, often with permanent losses on competitive terms
    DDoS-triggered sustained 503 errorsCrawl budget waste, partial deindexation2–4 weeks if resolved quickly
    Magecart / skimming scriptsSafe Browsing warning, user confidence impact3–6 months for ranking recovery; brand trust takes longer

    What Security Configurations Silently Harm Your Clients' SEO Performance?

    This is where the real advisory value lives for agencies. The following misconfigurations exist in the blind spot between security and SEO teams — and they're rarely monitored from both perspectives.

    The most overlooked category is server response inconsistencies. A WAF returning 200 OK on a soft-block page causes Google to index security interstitials as legitimate content — meaning your client could end up with WAF challenge pages appearing in their SERPs without anyone realizing it.

    This connects directly to security header configuration, where the SEO implications are equally significant. HSTS preloading eliminates HTTP-to-HTTPS redirect latency — a performance and security win. But a misconfigured Content Security Policy can break rendering that Google depends on for indexation. The X-Robots-Tag header sits at the exact intersection of security and crawl governance, yet it's typically only discussed from one side.

    Similarly, robots.txt governance presents a dual challenge. The file is publicly accessible, which means it reveals exactly where sensitive paths are. Meanwhile, "hiding" URLs via robots.txt prevents crawling but not indexation — those URLs can still appear in SERPs via inbound links. The proactive approach is defense in depth: noindex directives plus authentication plus network-level access control.

    Finally, redirect governance is where security and SEO teams most often collide. Open redirects (CWE-601) are a documented vulnerability, yet redirect logic is the primary mechanism for domain migrations and canonicalization. When a client's security team removes redirects without SEO context, link equity flow breaks silently.

    How Should Agencies Build a Unified Web Governance Framework for Clients?

    The core argument is straightforward: your clients need a cross-functional Technical Web Governance approach — not more siloed assessments. And you're the one positioned to deliver it.

    Every security change should undergo SEO impact analysis. Every SEO implementation should get a security review. This dual-lens approach is what separates agencies that retain clients for years from those that lose them after one unexplained traffic drop.

    Security ActionSEO Impact to CheckWho Typically Owns ItGovernance Fix
    WAF rule deploymentVerified crawler bypass via reverse DNSSecurity / DevOpsRequire crawl monitoring for 72 hours post-deployment
    Redirect rule change or removalLink equity flow, canonical chain integritySecurity or EngineeringCentralized redirect governance with SEO sign-off
    Bot rate limiting adjustmentCrawl budget allocation, indexation velocitySecurity / CDN teamAllowlist verified bots; test with Google Search Console
    CSP header modificationJavaScript rendering for GooglebotSecurityTest with Google's URL Inspection tool before deploying
    TLS certificate or version changeCore Web Vitals, mixed content warningsDevOpsPre-deployment Lighthouse and mixed content scan

    With seeshare, you can map scan findings to specific security controls across your client portfolio and generate branded reports that demonstrate exactly where each site stands — positioning your agency as the one that catches what others miss.

    What's Coming Next: Edge Rendering, AI Crawlers, and Regulatory Pressure

    As of 2025, three converging forces are making security-SEO integration unavoidable.

    Edge rendering convergence. As rendering moves to CDN edge functions like Cloudflare Workers and Vercel Edge, security configuration becomes SEO configuration. Misaligned caching or header policies at the edge simultaneously create security issues and indexation failures.

    AI crawling governance. LLM training pipelines and AI Overviews create bot management decisions with dual implications — data scraping risk versus inclusion in AI-generated results. The decision to allow or block these new crawlers has both security and visibility consequences.

    Regulatory escalation. GDPR, CCPA, and the EU Digital Services Act (effective February 2024) mean that indexed PII-containing URLs are simultaneously security concerns, SEO liabilities, and regulatory considerations. Agencies that operationalize this integration early are well positioned to help clients meet compliance requirements while building customer trust — and to develop a meaningful service line differentiator.

    Frequently Asked Questions

    Does website security directly affect Google rankings?

    Yes. Google confirms HTTPS as a ranking signal and flags compromised sites via Safe Browsing. Indirectly, security incidents cause downtime, crawl errors, and malicious redirects that compound ranking losses. As of 2025, the overlap between security posture and organic visibility is tighter than ever.

    How do WAF misconfigurations impact Googlebot crawling and organic traffic?

    WAFs that rate-limit or serve JavaScript challenges to all bots — without verified crawler allowlisting via reverse DNS — can block Googlebot entirely. The result is crawl budget waste, deindexation, and organic traffic loss that can appear within days of a WAF deployment or rule change.

    How long does it take a hacked client website to recover its search rankings?

    Even after cleanup, trust signal rebuilding typically takes three to six months, with some sites experiencing permanent ranking losses for competitive terms. The recovery timeline depends on the severity of the compromise, how quickly it's detected, and whether remediation addresses both security and SEO dimensions simultaneously.

    How can agencies integrate security and SEO assessments for clients?

    Establish a unified web governance review where every security deployment includes crawl impact analysis and every SEO change gets security review. Prioritize verified bot allowlisting, centralized redirect governance, and standardized server response handling across all infrastructure layers. This becomes a recurring service, not a one-time project.

    Turning This Into Your Competitive Advantage

    Agencies that treat SEO and security as one discipline — not two line items on different proposals — are well positioned to build deeper, more durable client relationships. This week, you can start with three concrete actions: check whether your clients' WAFs are blocking verified crawlers, review their robots.txt files for sensitive path exposure, and confirm that WAF soft-blocks return proper status codes instead of 200 OK.

    seeshare gives you the platform to run these scans across your entire client portfolio, deliver branded reports that surface what's typically invisible, and help your agency address both rankings and security posture in a single engagement. Starting with a baseline scan on a client site gives you a clear, data-backed conversation starter about integrated web governance.

  • SEO After a Website Hack: Long-Term Ranking Damage & Recovery

    SEO After a Website Hack: Long-Term Ranking Damage & Recovery

    SEO recovery after a website hack is the structured process of restoring organic search visibility — including rankings, indexation, crawl budget, backlink integrity, and user trust signals — following a security compromise. According to Sucuri's 2023 research, 68% of hacked sites never fully recover their pre-compromise rankings, but agencies with structured recovery protocols consistently avoid this outcome. For agencies and MSPs managing client portfolios, this means a security incident extends well beyond the technical remediation — it's an ongoing challenge to organic visibility that requires deliberate, phased response. Here's a gap worth understanding for every agency owner: no major security framework — NIST, OWASP, CIS — treats SEO as a protected asset in incident response planning. Organic search is often your client's highest-revenue channel, yet it has no formal protection in the playbooks the industry relies on. SEO resilience is a website security outcome, and agencies that position it this way will lead the next wave of client advisory.

    How Does a Website Hack Destroy SEO Rankings?

    The SEO fallout from a compromise hits your clients across five interconnected vectors, and understanding these is what separates a reactive agency from an authoritative advisor. Google's Safe Browsing flags trigger interstitial warnings that cause click-through rates to plummet 60–95% — significantly reducing your client's visibility even while their pages technically still rank. Mass deindexation follows as Google's crawl-budget reallocation favors spam-injected URLs, starving legitimate pages of crawl attention. Simultaneously, attackers inject outbound links to pharmaceutical, gambling, or malware domains while the compromised site gets linked from spam networks, creating bidirectional toxic backlink signals. Spam URL generation — sometimes tens of thousands of doorway pages — dilutes topical relevance and wastes crawl budget. Finally, the degraded user experience drives bounce rates up and dwell time down, sending sustained negative engagement signals.

    An important nuance is that different hack types create fundamentally different SEO damage, requiring tailored recovery conversations with your clients. A Japanese keyword hack spawning thousands of indexed spam pages is a completely different problem than a redirect hack sending visitors to malicious sites, which is different again from a cryptomining script silently degrading Core Web Vitals through CrUX's 28-day rolling window. If you're advising clients on incident response, this nuance is what builds trust. For deeper context on the initial damage mechanics, our analysis of how website security breaches destroy SEO rankings covers the foundational relationship between compromises and organic visibility.

    The compounding nature is what makes this significant. Crawl budget gets reallocated to spam URLs while clean pages go unvisited. Google's slow recrawl cycles mean weeks of silent degradation. By the time your client's marketing team notices traffic dropping, the damage has been compounding for weeks — and earlier detection consistently correlates with faster, more complete recovery. This is precisely why tools like seeshare matter for your client portfolio: continuous scanning across multiple sites surfaces findings before they become ranking crises, giving you the detection speed that determines whether recovery takes weeks or quarters.

    Why Does SEO Damage Persist Long After Malware Removal?

    According to Search Engine Journal survey data from 2023, 55% of website owners reported recovery times of 3–9 months, and the Sucuri research team concluded that 68% never fully recover pre-compromise rankings. The speed of detection is the primary variable — a Backlinko study of 50 hacked sites found that 20% regained 90% of rankings within 2 months, suggesting recovery timelines vary significantly based on response speed, niche competitiveness, and hack severity.

    The hidden long-term effects are worth proactively discussing with your clients. Brand SERP contamination — "is [brand] safe" appearing in autocomplete — lingers indefinitely. Google Merchant Center suspensions can significantly impact e-commerce clients. Rich snippet and Knowledge Panel loss strips visibility features that took years to earn. Even email deliverability suffers from domain reputation damage. British Airways' Domain Authority was still 9% below pre-breach levels four years after their 2018 incident (Moz, 2022). A small business florist lost 65% of organic traffic for seven months from a single plugin finding.

    For agency owners, the takeaway is structural: security teams and SEO teams operate in silos, and your clients' incident response playbooks almost certainly don't include SEO remediation steps. This is your advisory opportunity. The cost implications are significant — understanding how security incidents impact small businesses helps you frame this conversation in terms your clients understand.

    SEO ConsequenceRecovery TimelineDetection Dependency
    Safe Browsing flag removalIndustry estimates suggest 2–4 weeks after cleanupImmediate if monitored
    Organic traffic restoration3–9 months typicalFaster with pre-incident baselines
    Domain Authority recovery6–18 monthsOften incomplete
    Brand SERP contaminationIndefiniteRequires active reputation management
    Crawl budget normalizationIndustry estimates suggest 4–8 weeksRequires spam URL purge

    What Should an SEO Recovery Plan Include After a Client's Site Is Compromised?

    The dominant approach — fix the vulnerability, restore a backup, assume SEO self-corrects — fails consistently. Here's the phased approach you should be advising your clients on, and ideally building into your service agreements.

    During the first three days of emergency triage, your team should conduct a full-site crawl with Googlebot UA spoofing before restoring backups, as this preserves both forensic and SEO evidence. Alongside this, a Google Search Console Security Issues assessment and backlink baseline export from GSC, Ahrefs, and Majestic provide the data foundation for recovery, while server log analysis maps all attacker-created URLs to establish the full scope of compromise.

    The cleanup phase spanning days four through thirty centers on returning proper 410 status codes for spam URLs rather than soft 404s, which Google treats differently and may keep indexed for months. During this window, regenerate and submit comprehensive XML sitemaps containing only legitimate URLs, and file a precise disavow file targeting confirmed toxic backlinks. Equally important is scanning for canonical tag injection, robots.txt modification, structured data poisoning, and hidden sitemap files that may be directing Googlebot toward spam URLs — each of these represents a distinct vector that can sustain SEO damage even after the primary malware is removed.

    The authority rebuilding phase from days thirty-one through ninety is where the most value is created. Reconsideration requests should only be submitted after complete cleanup, since premature submission leads to denial and resets the queue timer by 2–4 weeks. Throughout this phase, daily crawl stat monitoring, systematic rebuilding of damaged internal link structures, and real-time indexation monitoring that detects reinfection before other security tools do are all essential to compressing recovery timelines.

    A critical trade-off to discuss with clients: aggressive disavow files risk 10–30% secondary ranking drops from accidentally disavowing legitimate links. Precision matters more than speed in this phase. Industry estimates suggest cross-referencing GSC and Ahrefs exports against server log timestamps isolates attack-generated links from legitimate ones — this hack-specific scan workflow is something virtually no generic toxic backlink guide covers.

    Why Should Agencies Treat Website Security as an SEO Strategy?

    The threat landscape is accelerating in ways that make proactive scanning essential to your SEO service offering. As of 2025, AI-powered spam injection uses LLMs to generate contextually relevant content that evades pattern-based detection. Google's increasing reliance on entity-based trust means a compromise can suppress an entire brand entity across Knowledge Panels, Discover, and AI Overviews — not just traditional blue-link rankings. The OWASP Top 10 for 2025 — which industry estimates suggest reflects this evolving landscape —, and understanding it positions you as the advisor your clients need.

    The preparation advantage is where agencies differentiate. Quarterly backlink baselines, documented SEO KPI benchmarks, and pre-authorized SEO participation in incident response plans compress recovery from quarters to weeks. This is work you can productize — and it costs less than a client lunch per month while giving your clients visible proof of protection.

    Preparation StepCostRecovery Impact
    Quarterly backlink baseline exportsMinimal (tool time)Enables precise disavow targeting
    Pre-incident SEO KPI documentation1–2 hours/quarterProvides recovery benchmarks
    Continuous security scanningLow monthly costReduces detection time from weeks to hours
    SEO steps in IR playbookOne-time setupPrevents the silo problem that causes 68% failure

    With seeshare, you can establish these baselines across your entire client portfolio, running scans that map findings to specific security controls and generating branded reports you deliver under your agency's name. This transforms security from a reactive cost center into a proactive SEO insurance policy — and a recurring revenue stream for your agency.

    Frequently Asked Questions

    How long does it take to recover SEO rankings after a website hack?

    The data shows significant variation. As of 2023, 55% of site owners report 3–9 months for meaningful recovery, while sites with integrated security and SEO response protocols can compress that to 2–4 months. Speed of detection is the single most influential variable — agencies running continuous monitoring for their clients have a structural advantage.

    Does Google penalize hacked websites?

    Google applies both manual actions (explicit penalties requiring reconsideration requests) and algorithmic suppression (automatic demotion based on trust signals). These are fundamentally different mechanisms with different recovery paths. Manual actions are visible in Search Console; algorithmic suppression is silent and harder to diagnose.

    Will disavowing backlinks help after a hack?

    Yes, but precision is critical. Over-aggressive disavow files that accidentally include legitimate referring domains cause secondary ranking drops of 10–30%. The key is cross-referencing backlink exports against server log timestamps to isolate attack-generated links from organic ones.

    Why is my client's website still losing traffic months after malware removal?

    The most common causes are index pollution from cached spam pages, lingering toxic backlinks that haven't been disavowed or processed, and slow algorithmic trust rebuilding. Google's recrawl cycles take weeks, and as John Mueller noted, partial fixes often delay recovery by months.

    Does website security directly affect SEO rankings?

    Beyond HTTPS signals, yes. Core Web Vitals degradation from injected scripts, Safe Browsing flags, and E-E-A-T trust erosion all directly suppress organic visibility. For a broader perspective, our piece on website security as a marketing problem explores this intersection in depth.

    Turn SEO Resilience Into a Client Retention Strategy

    The agencies that will retain and grow accounts in 2025 are the ones treating website security as an SEO strategy — not a separate concern. Add SEO assessment steps to your incident response playbooks this week. Establish quarterly backlink and ranking baselines for every client. Deploy continuous scanning that catches compromises before they become ranking crises.

    seeshare gives you the infrastructure to do all three at portfolio scale — automated scanning across client sites, branded reporting that demonstrates ongoing value, and the detection speed that determines whether a compromise costs your client a few days of visibility or a few quarters of revenue. Run a baseline scan on a client site today to see exactly where they stand, and start turning security posture into the trust signal that keeps your clients renewing.

  • How Website Security Breaches Destroy SEO Rankings

    How Website Security Breaches Destroy SEO Rankings

    Website security is a direct ranking factor in organic search — compromises like malware injection, SEO spam, and Safe Browsing flags degrade search visibility through both algorithmic penalties and user trust erosion. Understanding how security compromises affect search visibility — and how quickly — lets agencies position themselves as proactive advisors rather than reactive fixers. Security is not peripheral to SEO; it is structural to search visibility. For agencies and MSPs managing client websites, this intersection represents one of the most overlooked advisory opportunities in 2025. Most organizations treat security and search performance as separate disciplines, staffed by separate teams, tracked by separate dashboards. But the effects of an active compromise don't stay in a security silo — they show up directly in the search results your clients depend on for revenue.

    Think of it as "SEO debt." Just like technical debt in software, security neglect accumulates invisible ranking risk that compounds silently. The median compromise dwell time exceeds 70 days according to Sucuri's annual reports. Understanding that detection timeline helps you build monitoring practices that catch issues early, often within days rather than months. If you're the agency managing that site, the opportunity is in positioning your team to identify and address these issues proactively, turning security monitoring into a visible client service.

    How Does Google Actually Evaluate Website Security in 2025?

    HTTPS adoption is effectively universal among serious businesses — a 2023 Cloudflare Security Report found 95% of large enterprises have migrated, and Chrome has labeled HTTP sites "Not Secure" since 2018. If a client hasn't made the switch, it's a quick win, but it's not where the real risk lives. HTTPS is table stakes for the conversation, not the substance of it.

    The most significant ranking risk factor is Google Safe Browsing, which protects Chrome, Firefox, and Safari — roughly 85% of browser market share. When Safe Browsing flags a client site, users see a full-screen interstitial warning that reduces click-through rates dramatically. Google's Senior Search Advocate John Mueller stated in an April 2023 Q&A: "Security issues like malware or hacked content can tank your rankings overnight. Fix them fast, or you're invisible." This reinforces why proactive monitoring matters — catching compromises early limits the ranking impact and keeps recovery timelines short. Simultaneously, Googlebot may reduce crawl frequency or deindex affected pages entirely.

    What competitors consistently miss is the E-E-A-T and YMYL connection. Google's quality rater guidelines explicitly tie security to trustworthiness. For client sites in finance, healthcare, and e-commerce — categories Google classifies as "Your Money or Your Life" — a compromise doesn't just trigger a technical penalty. It fundamentally undermines the trust signals those sites need to rank at all. A 2023 MIT Sloan study found that sites with security warnings lose 30–50% of potential clicks from user distrust alone, compounding algorithmic losses with behavioral ones.

    There's also an angle that virtually no existing content covers: Core Web Vitals degradation from client-side attacks. Cryptominers, malicious JavaScript injections, and resource hijacking directly tank performance scores — Largest Contentful Paint, Interaction to Next Paint, and overall page speed. If you're running CWV assessments for clients without checking for malicious scripts, you may be optimizing around a problem you haven't identified. Tools like seeshare automate scanning across multiple client sites, catching these issues before they show up as mysterious performance regressions in your SEO dashboards.

    How Does a Security Compromise Affect Organic Traffic? 9 Damage Vectors

    Most guidance covers two or three ways security impacts SEO. The actual impact surface is far more extensive — and understanding the full taxonomy is what lets you advise clients with authority rather than generalities.

    Damage VectorSEO ImpactSeverity
    Safe Browsing warnings78% of users avoid flagged sites (Pew Research, April 2023); CTR collapses to near zeroCritical
    Page deindexationGoogle routinely deindexes compromised pages (confirmed March 2023 Search Central post)Critical
    SEO spam injectionPharma hacks, Japanese keyword hacks inject thousands of spammy pages, diluting topical authorityHigh
    Malicious redirectsHijacked redirects funnel PageRank to attacker domains, redirecting link equity away from the client siteHigh
    Crawl budget wasteGoogle's October 2023 Spam Update slashed crawl budgets by up to 30% for compromised sites (Search Engine Journal, November 2023)High
    Anchor text and internal link pollutionInjected links warp the site's internal linking signalsMedium
    Negative user behavior signalsBounce rate spikes, dwell time collapses send negative quality signalsMedium
    Backlink lossReferring sites delink from flagged domains, eroding off-page authorityMedium
    Long-term domain trust erosionWorst case requires domain migration — a 6–18 month process with no guaranteed outcomeSevere

    The compounding effect matters most here. A pharma hack doesn't just inject spam pages — it affects crawl budget allocation, dilutes topical relevance, generates toxic backlinks, and can eventually trip Safe Browsing flags. When a client reports a traffic drop, multiple damage vectors are often already in play. This is exactly the kind of compounding risk that regular website security assessments are designed to catch early.

    How Fast Do Rankings Drop — and How Long Does Recovery Take?

    This is the highest-value question in client conversations, and it's one that no top-ranking competitor answers with specifics. Recovery timelines vary dramatically by attack type, and setting accurate expectations is what separates strategic advisors from reactive fixers.

    Attack TypeTraffic ImpactTypical Recovery Timeline
    Safe Browsing blacklisting40–95% traffic loss within days2–4 weeks minimum after cleanup
    Google manual action (spam injection)Industry estimates suggest 60–80% organic visibility loss4–12 weeks after reconsideration request
    Full spam injection with backlink contaminationIndustry estimates suggest progressive erosion, often 40–60%2–6 months for full restoration
    Severe domain trust compromiseNear-total organic loss6–18 months (may require domain migration)

    Real-world examples illustrate the stakes. Target experienced a malware redirect in 2021 that dropped organic traffic 25% over two months, requiring three months of remediation. FitLifeDaily, a small fitness blog, suffered pharmaceutical spam injection across 40% of its pages in 2023 — Google issued a manual action, indexation dropped 60%, and full recovery took six weeks even with expert intervention. Understanding that the median detection timeline exceeds 70 days helps you build the case for continuous monitoring — agencies that catch issues within days rather than months keep their clients' recovery timelines short and manageable.

    What Should You Do When a Client's Hacked Site Loses Rankings?

    Recovery follows a specific sequence, and missteps reset the clock. When a client's site is compromised, your agency needs to execute an incident-response framework, not a generic tips list.

    First, contain and baseline. Isolate compromised files immediately and verify that any backups predate the initial compromise — restoring from a post-compromise backup reintroduces the problem. Simultaneously, document current rankings, indexed page counts, and traffic levels. This baseline is essential both for measuring recovery and for showing the client exactly what happened.

    Then clean and request review. Deploy server-side scanning to remove all injected content, backdoors, and unauthorized files. Here's the critical step most people miss: Google does not automatically clear Safe Browsing warnings or manual actions after cleanup. You must explicitly submit a reconsideration request through Google Search Console. Submitting prematurely — before thorough cleanup — triggers a rejection that resets the review clock.

    Finally, remediate and monitor. Disavow toxic backlinks generated by spam injections, but carefully — overly broad disavow files strip legitimate link equity. Accelerate recrawling via the URL Inspection tool and updated sitemaps. Then monitor weekly using site: searches. An unexplained index spike — say, from 500 pages to 15,000 — signals reinfection.

    Understanding common exploit patterns, like those outlined in the OWASP Top 10, helps your team identify root causes so the same exploit doesn't recur. And if you need a framework for positioning security as a core marketing concern during these conversations, the case is straightforward — clients who've been through a recovery timeline understand the value of proactive monitoring immediately.

    How Do You Build a Proactive Security-SEO Monitoring Stack for Clients?

    No single tool bridges the security-SEO gap. The optimal approach combines server-side scanning (Sucuri, Wordfence) with a WAF that includes Googlebot whitelisting (Cloudflare), Google Search Console for native security issue detection, SEO scanning tools (Ahrefs, Semrush) for index anomalies and toxic backlink detection, and file integrity monitoring at the server level. One critical caution: aggressive WAF rules and bot filtering commonly block Googlebot — a self-inflicted crawlability wound. Always verify Googlebot access via reverse DNS.

    With seeshare, you can layer proactive scanning across your entire client portfolio and generate branded reports that translate security findings into terms clients understand — including the SEO implications. Running a baseline scan before a client pitch demonstrates immediate value and gives you concrete findings to discuss, not hypothetical risks. Monthly monitoring then becomes a retention tool: clients who see regular, clear reports on their security posture are clients who understand what you're protecting.

    For agencies serving small business clients facing security incidents, this proactive approach costs less than a client lunch per month and provides visible, ongoing proof of protection — delivering clear value compared to the cost and effort of a multi-month SEO recovery.

    FAQ Section

    Can malware or hacking cause a website to lose Google rankings?

    Yes — Google deindexes compromised pages, reduces crawl rates, and triggers Safe Browsing warnings that significantly reduce click-through rates. Understanding the scope of potential impact (documented traffic reductions range from 40–95%) helps agencies prioritize proactive monitoring and set clear expectations with clients.

    How long does it take to recover SEO after a website hack?

    It depends on the attack type. Safe Browsing flag removal takes 2–4 weeks minimum after cleanup. Manual action recovery averages 4–12 weeks. Full traffic restoration from spam injection with backlink contamination takes 2–6 months.

    Does website security affect Core Web Vitals?

    Yes. Modern client-side attacks — cryptominers, malicious JavaScript, resource hijacking — directly degrade page speed and Core Web Vitals scores. This intersection is virtually uncovered in existing competitive content yet represents a growing attack vector as Google tightens performance-based ranking signals.

    How do I check if Google has flagged a client's site for security issues?

    Use the Security Issues report in Google Search Console, Google's Safe Browsing Site Status tool, and third-party scanners. Cross-referencing multiple sources catches issues that any single tool might miss.

    What's the biggest mistake agencies make during SEO recovery from a hack?

    Submitting a reconsideration request before thorough cleanup. A rejected request resets the review clock, extending the recovery timeline by weeks. Always confirm complete remediation — including backdoor removal and file integrity verification — before requesting review.

    Where This Leaves Your Agency

    The agencies that will maintain client search visibility through 2025 and beyond are those bridging security and SEO into a single discipline — not treating them as separate line items on a services menu. Every client conversation about organic performance should include security posture. Every SEO dashboard should track index count stability, GSC security alerts, and Safe Browsing status alongside keyword rankings and traffic trends.

    seeshare gives you the infrastructure to deliver this as a managed service. Run baseline scans on prospect sites to demonstrate value before the engagement starts. Deliver branded, ongoing monitoring reports that make security posture visible and understandable. When a client asks "why should we keep paying for this?" — the answer is the rankings, traffic, and revenue that proactive monitoring quietly protects every month.

    Start with one client site. Run a scan with seeshare, review the findings, and bring them to your next client conversation. That's how you move from reactive agency to strategic security partner — one clear report at a time.